

打造卓越软件
让我们一起创造非凡。
Lasting Dynamics 提供无与伦比的软件质量。
穆罕默德·布克里姆
11 月 04, 2026 • 9 min read
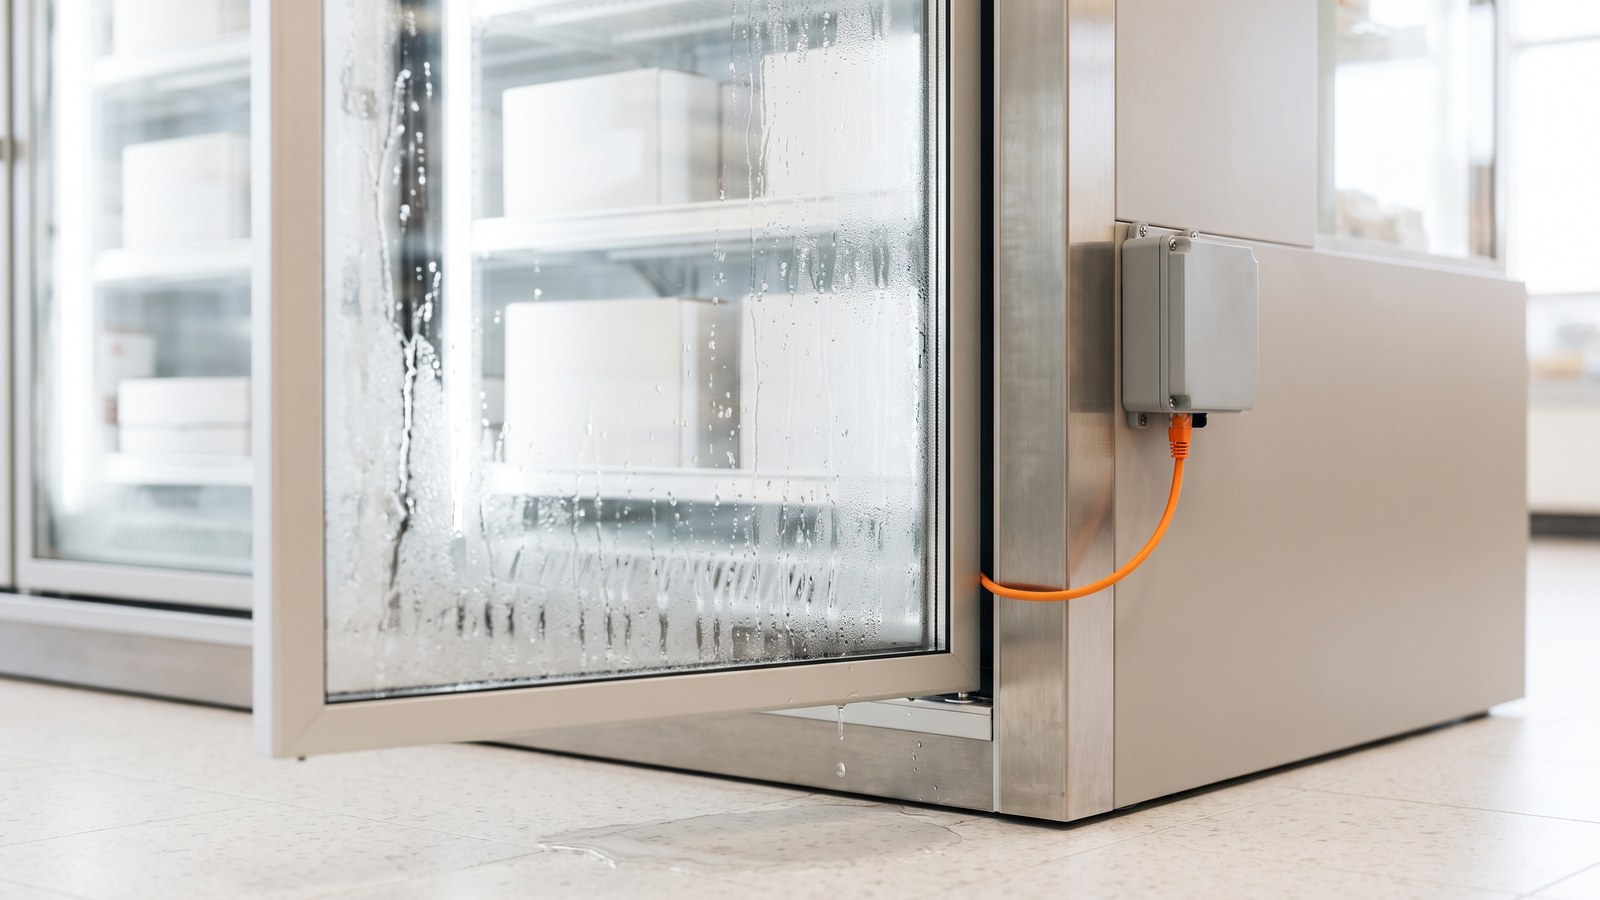
On the night of 11 October, refrigeration controllers in hundreds of French supermarkets were switched into defrost mode with the food still inside. Temperatures in some units climbed as high as 50°C and the heat caused fires in some stores, while whole aisles of fresh and frozen produce went in the bin, a scene repeated across Europe three weeks later.
None of it required genius: by the manufacturer's own account, most affected controllers were older models without security updates, reachable from the internet because that is how contractors maintain them. That is OT security in miniature, failing long before the firewall, in a purchase order that never asked when support ends and in a maintenance contract that never said who may connect, and how. What follows separates what is known from what is not, then draws three lessons for anyone who buys, runs or builds connected equipment.
France's national CERT published alert CERTFR-2026-ALE-012 on 12 October and updated it on 13 and 16 October. It reports “numerous compromises” of remote refrigeration controllers across four product lines, the Danfoss AK-SM and AK-SC series, Copeland XWEB and Dixell XWEB, and warns that attack campaigns against these devices are probably still under way. The Copeland and Dixell products were added in the 13 October update, which is a reminder that this is not one vendor's problem.
The chains' own early figures give a sense of the scale. Les Mousquetaires, which owns Intermarché, counted about 150 stores, Carrefour about 80, Coopérative U 80 of its 2,000 and Monoprix about 5% of its 490. Other outlets reported higher counts in the days that followed. Danfoss told Cooling Post that most of its affected units were legacy products that no longer get software or security updates, the AK-SM 800 and AK-SC 355, and that the newer AK-SM 800A units that were hit ran outdated firmware.
The second wave, at the start of November, hit stores in Belgium, Luxembourg, Estonia and Sweden, while Finland investigated similar cases, and later reports added the Netherlands, Ireland, Italy and Portugal. Three questions are still open: who is behind it, exactly how they got in and whether the November wave belongs to the same campaign. The companies and officials who have spoken all describe it as deliberate. Carrefour Belgium called it “a cyberattack, there is no other reason”, and EU Agriculture Commissioner Christophe Hansen spoke of “a deliberate attempt to disrupt” the food supply.
The pattern is not new either. A Danfoss newsletter had already cited attacks in 2022 on 16 Russian supermarkets and 40 Israeli stores, all without proper firewall or VPN protection. What changed in 2026 is the scale.
Operational technology (OT) security protects the systems that monitor and control physical equipment and processes, such as refrigeration, heating and ventilation, production lines, pumps and building management. When OT is compromised, the damage shows up in the physical world as spoiled stock, stopped lines or fires, not only as lost data.
That changes the priorities, because an office laptop is patched monthly and replaced every few years, whereas OT security starts from the opposite assumption, that the equipment must keep running and will stay in service as long as the room it cools. The fridge hack shows how long that can be, since Danfoss itself says the AK-SC 355 was phased out in 2016 and the AK-SM 800 reached end of life in 2021, yet both families were still controlling cold rooms this autumn.
IoT security and OT cybersecurity overlap without being the same thing. IoT describes a class of device, small and connected, while OT describes a function, controlling something physical. A store refrigeration controller is both, which is why classic IoT security failures such as default credentials now have physical consequences.
The weakest point in OT security is a date, the day support ends, and it is easy to leave out of a purchase order. CERT-FR is blunt about the consequences. Keeping an end-of-life device without security patches exposed to the internet means a very high probability of compromise. A factory reset removes the attacker's foothold, but the device stays vulnerable and, in CERT-FR's words, will certainly be compromised again.
End-of-life software is familiar in office IT, but in OT it is harder, because nobody swaps a refrigeration controller over a weekend. The buyer's lesson is therefore commercial before it is technical, since the price of connected equipment includes its support period. We would ask, in writing, for the end-of-support date and what happens after it, whether a replacement path, network isolation or a paid extension. That planning is the core of any legacy system modernization, and it applies to the plant room as much as to the ERP.
让我们一起创造非凡。
Lasting Dynamics 提供无与伦比的软件质量。
Regulation now pushes on the manufacturer's side through the EU Cyber Resilience Act (Regulation (EU) 2024/2847), which requires a declared support period that reflects the product's expected use time and, under Art. 13(8), lasts at least five years unless the product is expected to be in use for less. Art. 13(9) adds that each security update must stay available for at least ten years or for the rest of the support period, whichever is longer, and our Cyber Resilience Act guide covers what this means for the teams that build products.
For the operator, the arithmetic still does not close, because five years is a floor and the Danfoss models above stayed in service long after their support ended. Even under the new rules, the gap between the end of support and the end of service is yours to manage.
The controllers were online for a sensible reason, and that reason had no owner. Engineering teams and contractors use remote access to troubleshoot without a site visit, which keeps maintenance costs down, and the same connectivity makes predictive maintenance possible, so the answer cannot be to unplug everything.
Yet refrigeration controllers are often assumed to be isolated when many are directly exposed, as Claroty's CTO Amir Preminger told The Register. In the week of the attack, Shodan, a search engine for internet-connected devices, listed more than 4,500 internet-facing Danfoss controller interfaces, over half of them in France. Not every exposed device was attacked, but every one was within reach.
The closest documented precedent is twelve years old: in November 2013, attackers entered Target's network with credentials stolen from Fazio Mechanical Services, an HVAC and refrigeration contractor, as Brian Krebs reported. By Fazio's own account, its connection was for electronic billing, contract submission and project management, not for running Target's climate systems, and it still became the way in for a breach in which, Target said, about 40 million card accounts may have been affected. A contractor's access is part of your attack surface, whatever it was meant to be for.
CERT-FR asks operators to remove the internet exposure and restore access only through a secure VPN or protected network, treating filtering on contractors' IP addresses as an emergency measure and not as a lasting fix. One detail says a great deal: operators should check their insurance terms before cutting the data link to their refrigeration contractor, because the remote connection is often written into commercial agreements nobody read with security in mind.
In OT security, secure remote access is a contract clause before it is a product, one that says who connects, through what path, who keeps the logs and when access is revoked. If the maintenance contract is silent on those points, the installer's habits decide.
A password you never set is not a control, and a hidden password is worse. In August, Claroty's Team82 published research on the AK-SM 800A that included CVE-2025-41450, rated 8.2 (high) on the CVSS v3 scale: a hidden “code-of-the-day” login checked against a value derived from the device's date instead of the administrator's password. Danfoss had already fixed it in firmware version 4.2, announced in March 2025, which is exactly why outdated firmware matters.
Investigators have not tied this specific flaw to October, but it is the kind of door that turns device security into reading the calendar. Security researcher Kevin Beaumont told The Register that exploiting it was "a zero-skill thing to pull off".
从创意到发布,我们根据您的业务需求量身打造可扩展的软件。
与我们合作,加速您的成长。
Default credentials have a well-documented history in OT. One of the clearest cases came in November 2023, when attackers took over a Unitronics controller at a booster station of the Municipal Water Authority of Aliquippa, in Pennsylvania, which regulates water pressure for two townships. CISA's alert on the Unitronics attacks urged operators to make sure the default password, “1111”, was no longer in use, and a joint advisory in December 2023 blamed weak passwords and exposure to the internet.
Three years and an ocean apart, CERT-FR's advice for refrigeration is much the same and costs little: update the firmware, set Danfoss controllers to the “Strict” security level and confirm that default passwords have been changed. For new products, the Cyber Resilience Act turns this into law. Annex I, Part I(2) requires products to reach the market without known exploitable vulnerabilities, with a secure by default configuration, protection from unauthorized access and a limited attack surface. A hidden login fails several of those tests at once. But the rule governs what is sold from December 2027, not the controller already bolted to the wall.
Regulation pushes hard on the companies that make connected products and hardly at all on those that run old ones. Under Art. 69(2) of the Cyber Resilience Act, products placed on the market before 11 December 2027 come under the regulation only if substantially modified, and Art. 69(3) makes one exception: the Art. 14 duties to report actively exploited vulnerabilities and severe incidents, which have applied since 11 September 2026, cover all in-scope products already on the market. The text is silent on devices declared end of life years ago, so the prudent course is not to count on it.
NIS2, Directive (EU) 2022/2555, is the other instrument people reach for, but its Annex II covers food businesses “engaged in wholesale distribution and industrial production and processing” and does not name retail. Depending on national transposition, a supermarket chain may have NIS2 duties for its cold-chain warehouses and none for the stores where these fridges sit.
That is not a failure of the rules, since regulation cannot retrofit a controller built in the 2010s. For the installed base, the only control that works is the operator's own inventory, and no law will compile it for you.
An afternoon is enough for a first OT security pass, starting with a search of your own IP ranges on Shodan or Censys to see which management interfaces answer from the public internet. A list of each connected controller's end-of-support date, with its firmware next to the vendor's latest version, then shows how old the installed base really is.
The people side takes longer. It means knowing who has remote access, through what path and when it was last reviewed, including every contractor and any contract or insurance clause that requires the link. It also means checking whether default passwords are still active and whether hardened modes, such as Danfoss's "Strict" level, are switched on.
The check also means asking whether anyone would notice, and how fast. At one ICA store in Stockholm, France 24 reported, the November attack happened at 2am and was noticed at 5:30am, which is why a change to a setpoint or a defrost schedule should reach a person out of hours. None of this needs a new tool, but every part of it needs an owner.
Do you know which of your connected systems will still be running after their software support has ended? Let's talk it through.
This article was written by Mohamed Boukrim at Lasting Dynamics, an EU-based custom software development company that also builds AI software. It is written for the people who buy, run or build connected equipment, because that is where the decisions that left these controllers exposed were made. The facts above are dated and linked to their sources, so you can check whether they still hold when you read this. The questions are yours to ask, and the answers are yours to act on.
我们设计并打造脱颖而出的高品质数字产品。
每一步都可靠、高效、创新。
OT security protects the systems that control physical equipment and processes, such as refrigeration, production lines and building management. Its first concern is keeping equipment running safely, because a compromise causes physical harm, as Europe's supermarkets found this autumn.
IT security protects data on systems that can be patched and replaced often. OT security protects physical processes on equipment that runs continuously for many years, so safety and uptime weigh more than confidentiality, and an update is planned like a maintenance stop.
Nothing points that way. The flaws documented in these controllers include a hidden login that experts call easy to script, and CERT-FR's advice is about basics: internet exposure, end-of-life firmware and default passwords.
Mostly not. Products placed on the market before 11 December 2027 are covered only if substantially modified (Art. 69(2)). The exception is the Art. 14 reporting duties, which apply to in-scope products already on the market (Art. 69(3)). Whether that reaches devices a manufacturer stopped supporting years ago is not settled.
They overlap. IoT security is about a class of connected device, OT security about the job a system does. When a connected device controls something physical, like a fridge controller, both apply.
将大胆的想法转化为强大的应用。
让我们一起创造出具有影响力的软件。

穆罕默德·布克里姆
我是一名软件工程师兼后端开发人员,始终致力于确保软件质量和构建稳健的架构。 我不相信捷径;卓越的成果是日常投入和辛勤工作的直接产物。 我与团队通力合作,运用敏捷方法论并持续评估流程,以此突破界限并优化性能。面对每一项挑战,我都秉持极强的竞争意识:我孜孜不倦地努力攀登巅峰,一旦登顶,便继续奋进以保持领先地位。.
